Continuity Guardian’s IT and Information Security Risk Assessment (ISRA) module ensures full compliance with best practices and the regulatory framework because it is designed to meet the requirements of the most demanding International Standards ISO27001, BS7799-3 & NIST SP 800-39.
Strengthen your InfoSec
- Classify systems based on Confidentiality, Integrity, Availability
- Manage and deploy questioners with ease Includes executive overview, workflows and email notifications.
- Assess controls and define Risk level, based on system classification & frameworks including NIST, ISO 27001, ISO 31000, and PCI and regulations including GDPR.
- Decide which risk treatment is better to implement, by comparing the residual risk from each action selected.
- Risks are compared against the designated Risk Appetite
Make it 100% Compatible to your needs
- Multiple Assessments Types allows you to ask exactly what you want, to exactly who you want.
- Extensive functionality and intelligent technologies allow you to implement exactly the methodology you need.
- Fine tuning of risk & Controls values, separately for each system using objective criteria or an expert opinion or just use the defaults.
- Execute what-if scenarios in every step of the process.
- Versioning allows unlimited and regular updates for every system.
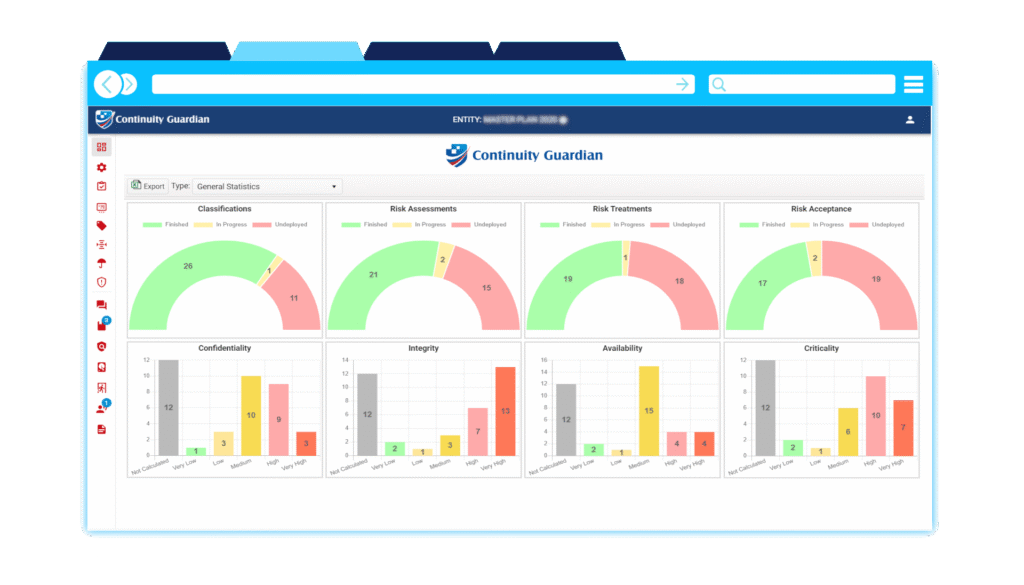
Develop a Real-time View to Manage Information Security Risk
- Specialized views and tools, to monitor remediation activities that enables to have overview on every phase of deployments.
- Flexible Dashboard that gives the ability to have overview per application and per standard you want.
- Very easy to get spreadsheet reports.
- Total transparency and accountability as everything is stored on a centralized system.